0
Not analyzed
Run the checker to evaluate cookie security.
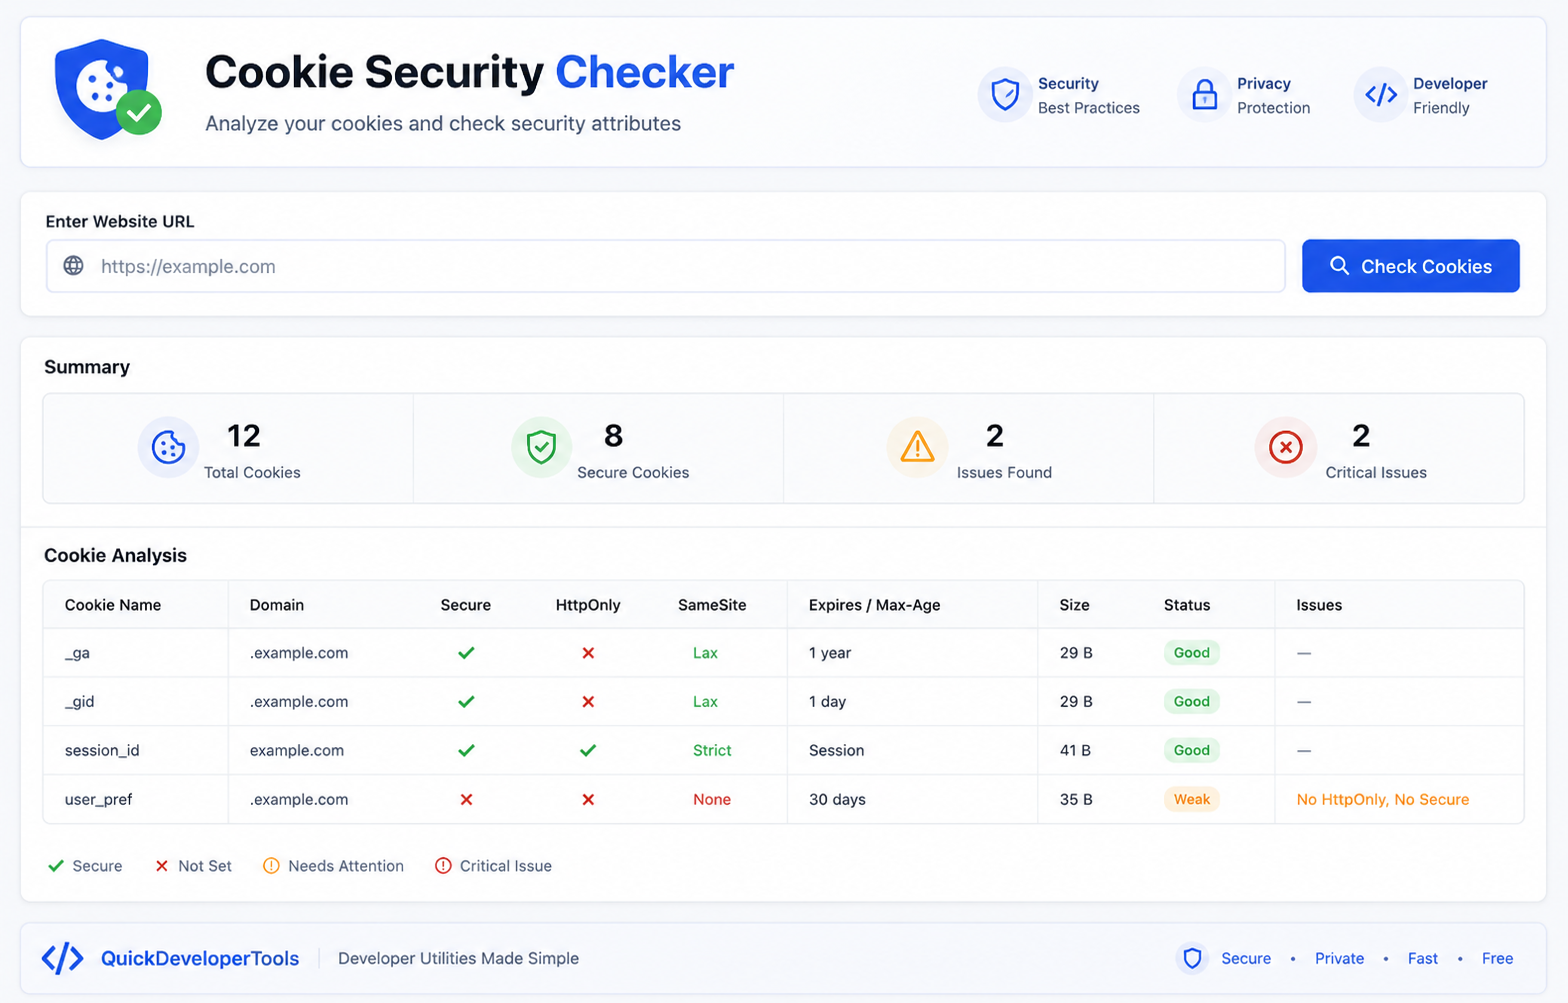
Inspect Secure, HttpOnly, SameSite, Domain, Path and expiration settings across one or more Set-Cookie headers.
This response carried no Set-Cookie header at all.
Nothing is wrong and nothing failed. A response with no cookies is the strongest
possible result for the checks this tool runs — there is no cookie that could
be missing Secure, missing HttpOnly, or set to
SameSite=None. Under GDPR and the ePrivacy Directive, setting no
non-essential cookie before consent is the behaviour that is actually required.
Set-Cookie, so edge-served pages usually have none by design.document.cookie writes never appear in a response header, so this check cannot see them. Your browser's DevTools → Application → Cookies can.Run the checker to evaluate cookie security.
Pasting Set-Cookie header values and analyzing them for Secure, HttpOnly, SameSite, prefix and expiration rules happens entirely in your browser - nothing is sent anywhere. Checking a live website is different: browsers deliberately hide the Set-Cookie response header from cross-origin JavaScript, so our .NET backend fetches the page instead and reads the raw Set-Cookie headers directly off the HTTP response (never a comma-merged approximation). The same SSRF protections used across our security tools apply here too - private, loopback, link-local and cloud-metadata addresses are always rejected, and every redirect hop is re-validated before being followed. The backend never stores or logs the cookie values it reads, and only response headers are fetched - the page body is never downloaded.
Related tools: Security Headers Checker · CSP Checker · CORS Checker
Modern browsers reject cookies marked SameSite=None unless they also have the Secure flag, so this combination usually means the cookie will silently fail to be set at all - a functional bug as much as a security one.
These are browser-enforced naming conventions: a __Host- cookie must have Secure, no Domain attribute, and Path=/, while a __Secure- cookie must have Secure set. Browsers reject a Set-Cookie header that uses the prefix without meeting its rules.
No. Hostnames that resolve to localhost, private IP ranges, link-local addresses or cloud metadata endpoints are rejected before any request is made, and each redirect hop is re-validated the same way.
No. Cookie values pass straight through the response and are never written to logs or storage - only the exception message is logged if a fetch fails, never response content.
By default, .NET's HTTP client would quietly absorb Set-Cookie headers into its own cookie store instead of surfacing them - and would carry cookies between requests. This tool disables that entirely so each check is stateless and the raw headers are always returned.